CYBERSECURITY • SECURITY OPERATIONS • VAPT

OFFENSIVE THINKING. DEFENSIVE EXECUTION.

Anoop
Ambrose_

Cybersecurity Practitioner / SOC Analyst in Progress

I bring a penetration-testing mindset to security operations — learning how attacks work, how telemetry exposes them, and how analysts investigate and respond.

SOC OperationsSIEM & DetectionIncident InvestigationPenetration Testing
Building hands-on security labsKERALA, INDIA
IDENTITY / 001● ACTIVE
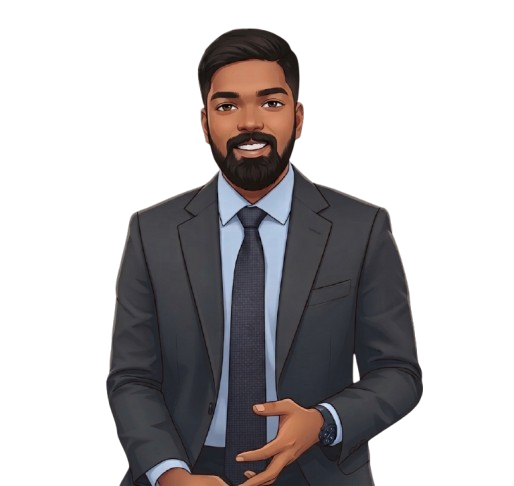
Portrait of Anoop AmbroseAA
ANOOP AMBROSECybersecurity • SOC • VAPT
⌁RED TEAMUnderstand the threat
◉BLUE TEAMDetect & investigate
09° / 76° SECURITY MINDSET
SCROLL TO EXPLORE
01 / THE APPROACH

One security discipline is stronger when it understands the other.

AA.

THE PERSON BEHIND THE TERMINAL

Curious about the attack.
Committed to the defence.

I find security weaknesses. I understand the threats. I work towards stronger defences.

I'm Anoop Ambrose, a Penetration Tester and Cybersecurity Practitioner passionate about understanding how systems are attacked and how they can be better protected.

My journey in cybersecurity started with offensive security, where I developed an interest in penetration testing, vulnerability assessment, web application security and network security. I enjoy exploring systems, identifying potential weaknesses and understanding the risks they create.

Today, I'm taking that knowledge further by developing my skills in Security Operations Centre (SOC) operations. I'm working with SIEM technology, particularly Splunk, to understand how security events are collected, monitored, investigated and turned into meaningful security insights.

I'm also building a hands-on SOC lab where I simulate security activities, collect endpoint logs from Windows and Linux systems, and investigate the resulting telemetry. This helps me understand both sides of a security incident: how an attack happens and how a defender can identify it.

What I bring to the table

  • Offensive security perspective: I approach systems with an attacker's mindset to identify weaknesses and understand potential risks.
  • Defensive security development: I'm building practical experience in SIEM monitoring, log analysis, threat detection and incident investigation.
  • Analytical thinking: I focus on understanding the evidence, investigating the cause and communicating technical findings clearly.
  • Continuous learning: I take initiative in building labs, testing tools and documenting what I learn.

Why work with me?

I bring curiosity, a practical mindset and an interest in both offensive and defensive security. Rather than looking at vulnerabilities in isolation, I want to understand their real-world impact, how they can be detected and what can be done to reduce risk.

My goal is to help organisations better understand their security weaknesses, recognise potential threats and build stronger defences.

I'm always open to cybersecurity opportunities, collaboration and learning from professionals in the industry.

My interests span security monitoring, SIEM workflows, alert triage, Linux and Windows telemetry, incident investigation, web application security and clear technical reporting. I value practical evidence over unsupported claims — build a lab, reproduce an activity, inspect the logs and document what happened.

CPTCertified Penetration Tester
RED + BLUEOffensive and defensive perspective
HANDS-ONLearning through practical labs
02 / AREAS OF FOCUS

Two perspectives.
One security objective.

My technical development connects the adversary's techniques with the defender's visibility, investigation and response.

01 / OFFENSIVE↗
⌘

Penetration Testing
& VAPT

Assessing attack surfaces, validating weaknesses and understanding how vulnerabilities can be exploited in authorised environments.

  • Reconnaissance & enumeration
  • Web application testing
  • Burp Suite & Nmap
  • Findings and remediation reporting
RED
02 / DEFENSIVE◎
⌁

SOC Operations
& Detection

Turning endpoint and network activity into useful security context through monitoring, triage and structured investigation.

  • SIEM & log analysis
  • Alert triage and prioritisation
  • Incident investigation
  • MITRE ATT&CK mapping
BLUE

03 / SELECTED WORK

Build. Simulate.
Detect. Investigate.

Practical environments are where offensive knowledge becomes defensive capability. Here is the lab I'm actively developing.

FEATURED LAB / 001 IN DEVELOPMENT

SIEM • ENDPOINT TELEMETRY • ATTACK SIMULATION

Multi-endpoint
Splunk SOC Lab

A home SOC environment designed to explore the full workflow: generate controlled security activity, collect endpoint telemetry, investigate events in Splunk and document findings from both attacker and defender perspectives.

SplunkUbuntuWindows 11Kali LinuxVirtualBox
Explore SOC project repository ↗
LAB TOPOLOGYENV / HOME SOC
⌘
OCTOPUSKali Linux / Test host
RED
CONTROLLED TEST ACTIVITY
▣
CITADELUbuntu endpoint
▣
BEACONWindows 11 endpoint
COLLECTED TELEMETRY
◉
SENTINELUbuntu / Splunk server
BLUE
ENDPOINTS CONNECTEDVIRTUAL LAB
i

Project integrity: This is a personal lab, not a production SOC. The architecture reflects the environment and setup progress described in the project documentation; detections, results and response metrics will be added as they are validated.

02 / WEB SECURITY

Web Application Security

Practice focused on identifying, validating and documenting common web application weaknesses in authorised learning environments.

BURP SUITE • OWASP
03 / NETWORK SECURITY

Network Reconnaissance

Building familiarity with service discovery, enumeration, network visibility and the security implications of exposed services.

NMAP • WIRESHARK

04 / WORKFLOW

From activity
to actionable insight.

A repeatable approach keeps security work measurable, explainable and useful to the people responsible for reducing risk.

01SIMULATE

Generate controlled activity in an authorised lab.

02COLLECT

Capture endpoint and system telemetry.

03INVESTIGATE

Correlate events, timelines and indicators.

04DOCUMENT

Record evidence, impact and recommendations.

TOOLS I WORK WITH AND CONTINUE TO DEVELOP

Technology is the tool.
Investigation is the skill.

SOC & Monitoring

SplunkSIEM conceptsLog analysisMITRE ATT&CK

Offensive Security

Burp SuiteNmapGobusterHydra

Systems & Network

LinuxUbuntuKali LinuxWindowsWireshark

Scripting & Workflow

PythonBashGitGitHub

06 / CREDENTIALS & DEVELOPMENT

Learning with
purpose and practice.

Credentials support the foundation. Continuous lab work, investigation and documentation build the capability.

CPT
CERTIFICATION

Certified Penetration Tester

CPT credential listed in my existing portfolio.

↗
C
COURSEWORK

Cisco Cybersecurity

Cybersecurity learning through Cisco Networking Academy coursework.

↗

07 / CONTACT

Let's talk security.

Interested in cybersecurity, SOC operations, practical labs or collaboration? Find me through the links below.

For project details and technical work, explore my GitHub repositories.